About Silver Fox
A Texas cybersecurity firm built to test assumptions.
Silver Fox LLC is a cybersecurity services and technology company headquartered in Frisco, Texas. We help organizations understand their risk, find their weaknesses, strengthen their systems and respond with confidence when something goes wrong.
Our work covers the full attack lifecycle, from strategy and compliance to penetration testing, security engineering, managed detection and incident response.
What we believe
Security is a connected problem.
Attackers do not see separate departments for cloud, identity, applications, networks and data. They see opportunities, and they move between them.
A vulnerable application can expose an identity. A compromised identity can open up cloud infrastructure. A weak configuration can turn limited access into full control. That is why we keep offensive testing, defensive operations and engineering under one roof, so a weakness found in one place improves security everywhere else.
Offensive insight
Knowing how attackers think changes how security is designed. Our testing looks past individual vulnerabilities to privilege, lateral movement and realistic impact, and the findings go on to improve architecture, identity controls and monitoring.
Defensive discipline
Good defense is knowing what matters. We build and run security operations around meaningful detection, threat context, careful investigation, clear escalation and continuous improvement, with fewer noisy alerts.
Engineering depth
Finding the weakness is often the start of the job. We redesign architecture, harden infrastructure, improve identity controls, integrate security tools and, where off-the-shelf products fall short, build what is missing.
How we think
Five principles behind every engagement.
- Evidence over assumption
- Confidence should come from what can be demonstrated.
- Context over volume
- More findings, alerts and data do not automatically make anyone safer.
- Paths over silos
- Individual weaknesses matter most when they combine.
- Engineering over theater
- Security work should improve the environment as well as the report.
- Clarity under pressure
- Technical depth should make decisions easier, especially during an incident.
Why Texas
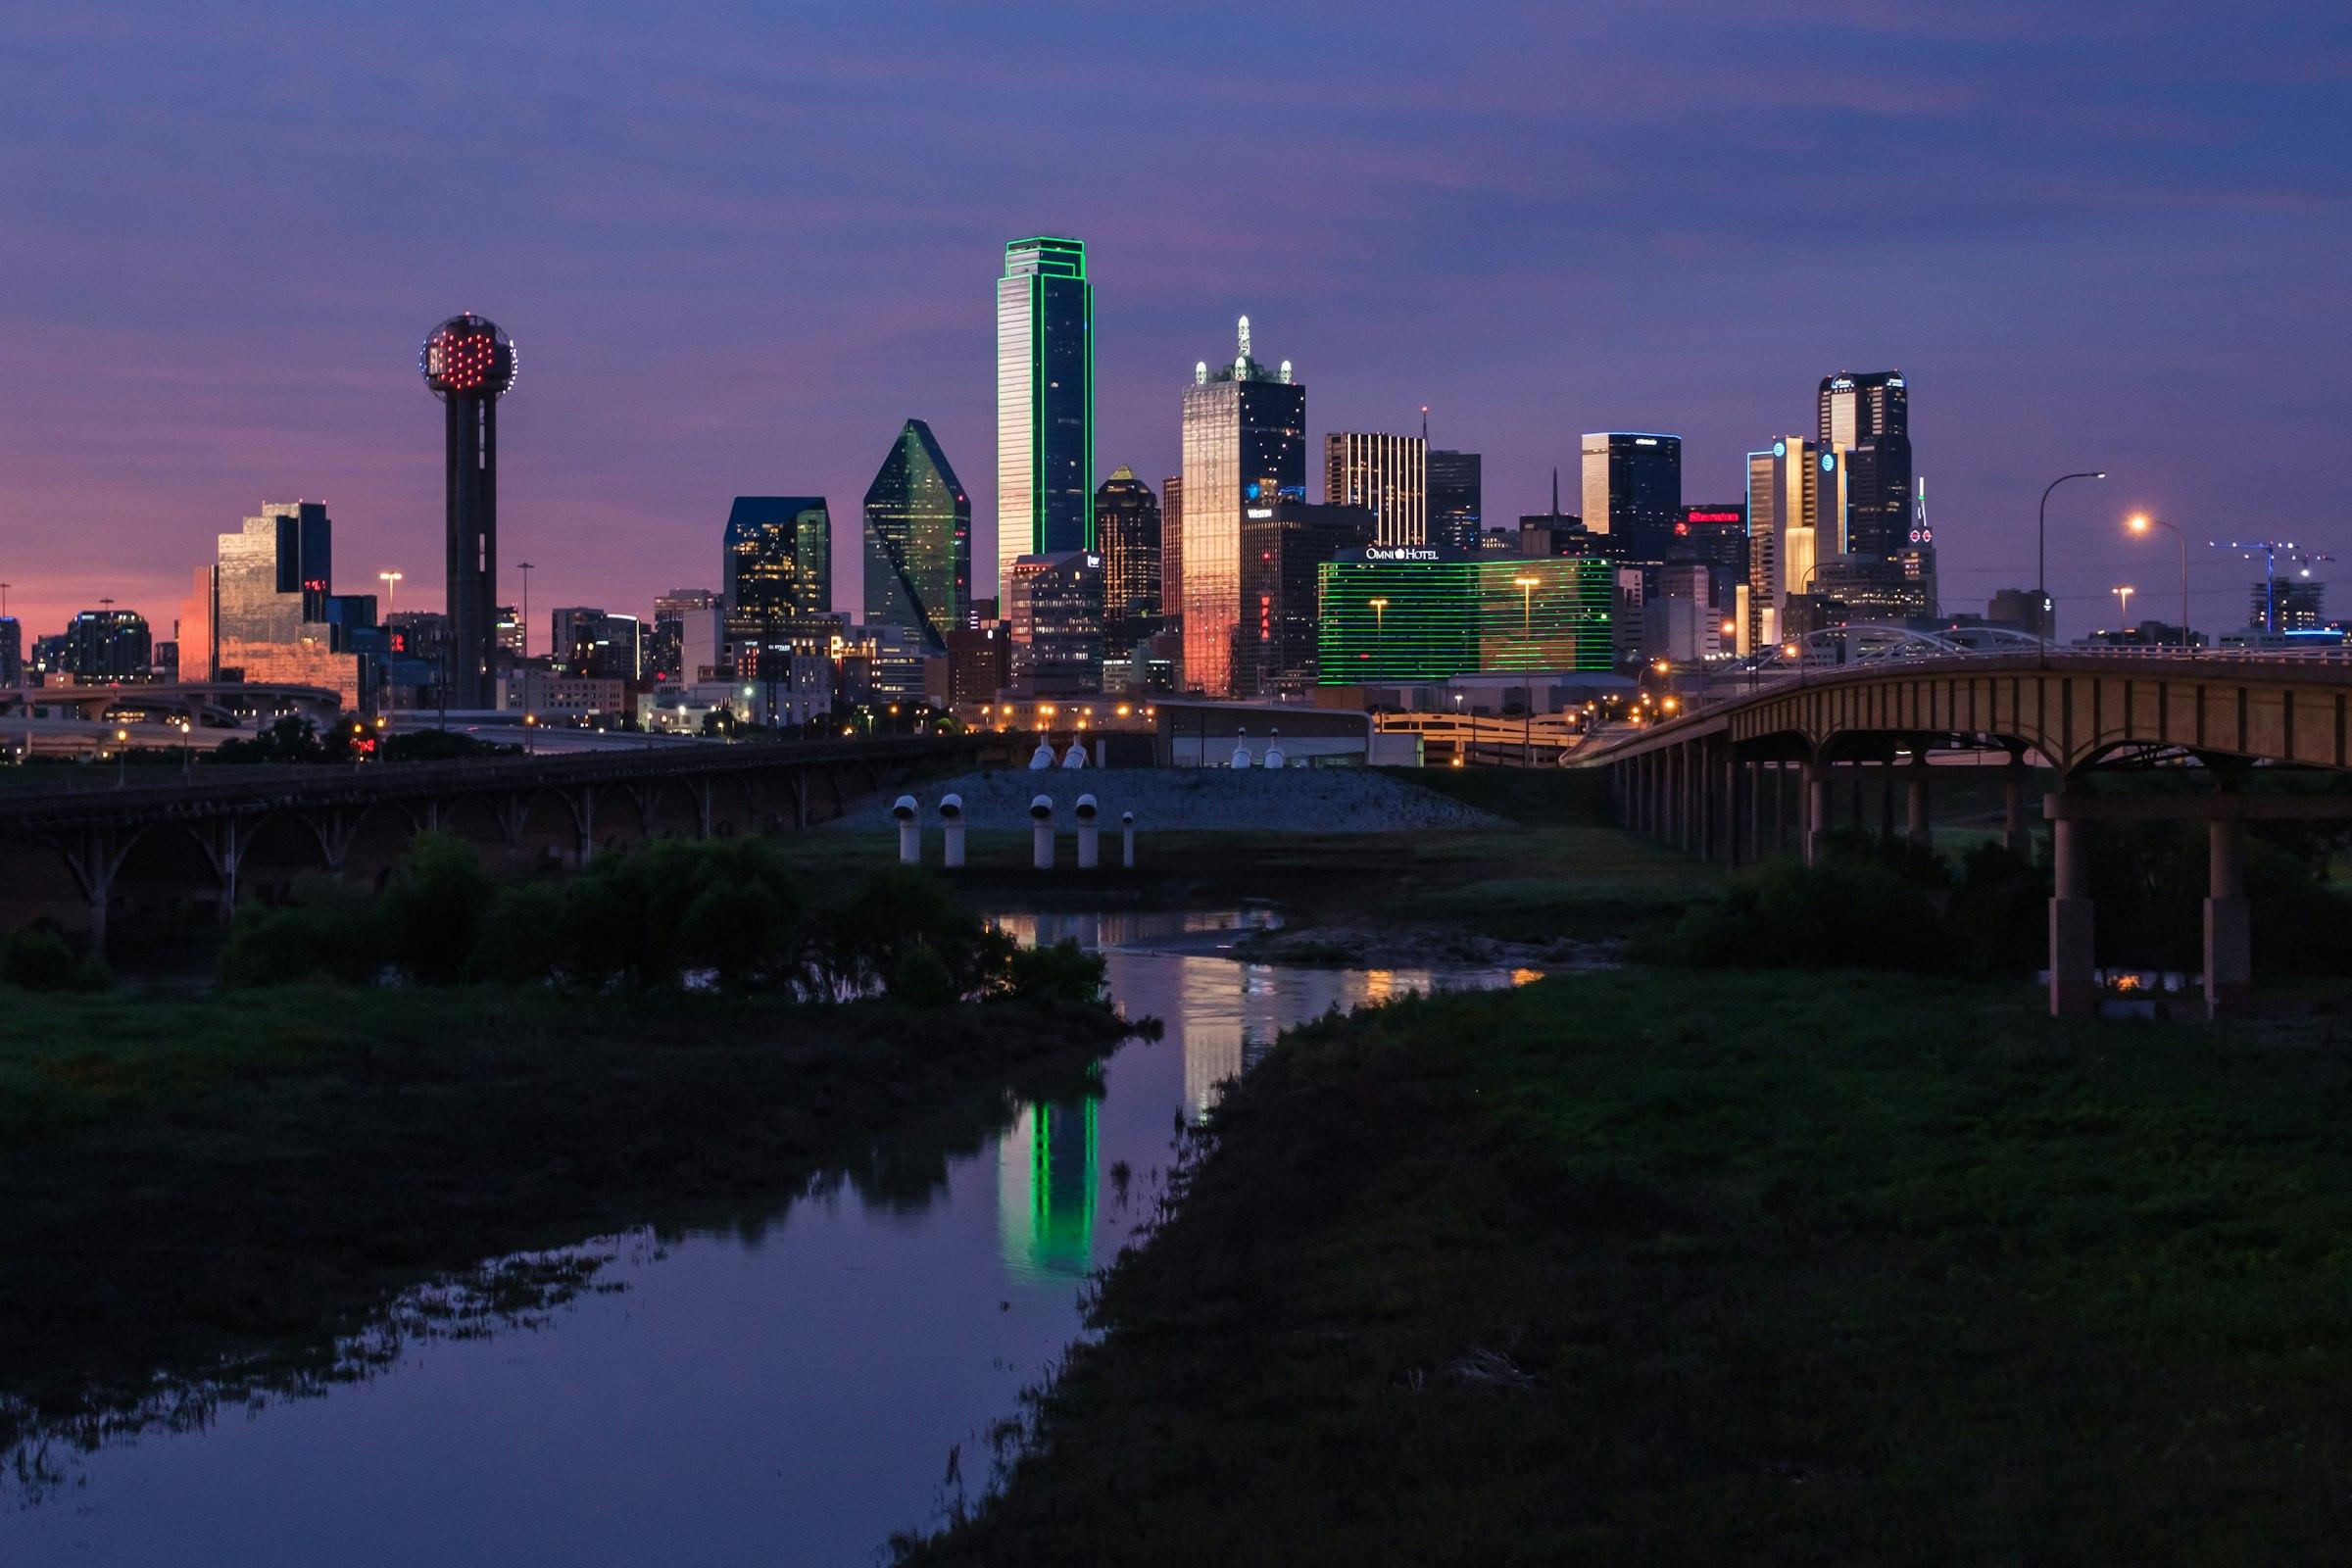
Close to the industries we protect.
Texas runs much of the country's energy production, a large share of its defense manufacturing, some of its largest hospital systems and one of its fastest-growing technology sectors. Those industries face serious, well-funded attackers.
Being based here means we know the state's regulators, industries and pace of business, and we can be on site when it matters. We also work with clients across the rest of the United States.
Our approach
Six steps we follow, whatever the engagement.
Each step feeds the next, and the last one feeds the first.
- 01
Understand
Build an accurate picture of the organization, its technology and the risks that matter.
- 02
Challenge
Test assumptions through technical assessment and adversarial thinking.
- 03
Engineer
Design and implement controls that reduce meaningful exposure.
- 04
Defend
Monitor, detect and investigate activity across the environment.
- 05
Respond
Contain incidents, establish the facts and restore control.
- 06
Improve
Turn findings, simulations and incident evidence into stronger security.
People and credentials
Every engagement is led by a practitioner.
The people who scope your engagement are the people who do the work. Our team holds industry certifications including OSCP, CISSP and CREST, and we keep those skills current through research, training and our own platforms.
Let's talk about where you stand.
If you want an honest view of your security and a practical plan to improve it, we would like to hear from you.